Malware & Ransomware
Remove Mac Malware: 8 Steps to Clean and Secure Your System
Most Mac infections hide in launch agents and browser extensions, not in obvious application folders, making standard deletion ineffective against persistent threats.
Most Mac infections hide in launch agents and browser extensions, not in obvious application folders, making standard deletion ineffective against persistent threats.
Firmware updates alter the static instructions embedded in hardware, creating a permanent risk window if the installation process is interrupted or tampered with.
Attackers often compromise build artifacts before deployment, leaving runtime defenses blind to the initial breach vector.
Default server configurations often expose file structures, turning your web server into an open directory for automated scanners to index and exploit.
Remote access trojans hide inside legitimate software to give attackers persistent control over your system without triggering standard antivirus alerts.
Validating the cryptographic signature of DNS responses prevents attackers from redirecting your traffic to malicious servers without user interaction.
Federated identity shifts trust from passwords to cryptographic assertions, creating a single point of failure that attackers target with precision rather than brute force.
Keeping data longer than necessary increases your attack surface and legal liability without providing operational benefit to your organization.
Zero Trust replaces the castle-and-moat model with continuous verification, ensuring that every request is treated as hostile until proven otherwise, regardless of location.
Multi-factor authentication stops stolen passwords but fails if the second factor is intercepted or if the user is coerced into bypassing it.
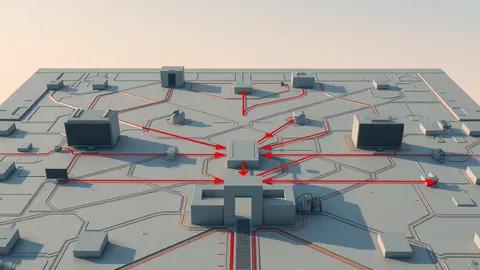
You can stop breaches by mapping the chain of steps attackers use, revealing hidden weak links that single-point defenses miss entirely.
A single misconfigured role can turn a read-only service account into a full administrator within minutes.
Deception technology turns your entire network into a trap by placing high-fidelity fake assets that attackers mistake for real targets, triggering immediate alerts on interaction.
Attackers steal valid data packets and resend them to trick systems into granting unauthorized access or repeating transactions.
Zero Trust Network Access replaces network perimeter trust with continuous, granular identity verification for every single request.
Golden images reduce deployment time but introduce a shared attack surface that amplifies the impact of any single compromise across your entire infrastructure.
Honeypots generate high-fidelity data by design because every interaction is unauthorized, eliminating the noise that drowns out signals in standard logging.
The National Vulnerability Database serves as the centralized catalog for security flaws, providing the unique identifiers that drive automated patching workflows across the industry.
Most invoice fraud bypasses visual checks by exploiting trusted vendor relationships and subtle email header inconsistencies that standard filters ignore.
Secure access service edge fails when organizations treat it as a perimeter replacement rather than an identity-centric enforcement layer, leaving lateral movement open.
SIM swap fraud bypasses perimeter defenses by hijacking the identity channel, leaving distinct anomalies in authentication logs rather than network traffic patterns.
Database security controls often create operational friction that slows legitimate business processes while leaving metadata exposed to determined attackers.
Recovery time objective forces you to choose which systems survive an attack and which you accept losing, turning chaos into a calculated trade-off.
Cloud workload protection agents intercept system calls at the kernel level to block exploitation before the operating system processes the request, hiding the defense from the attacker.